What happened
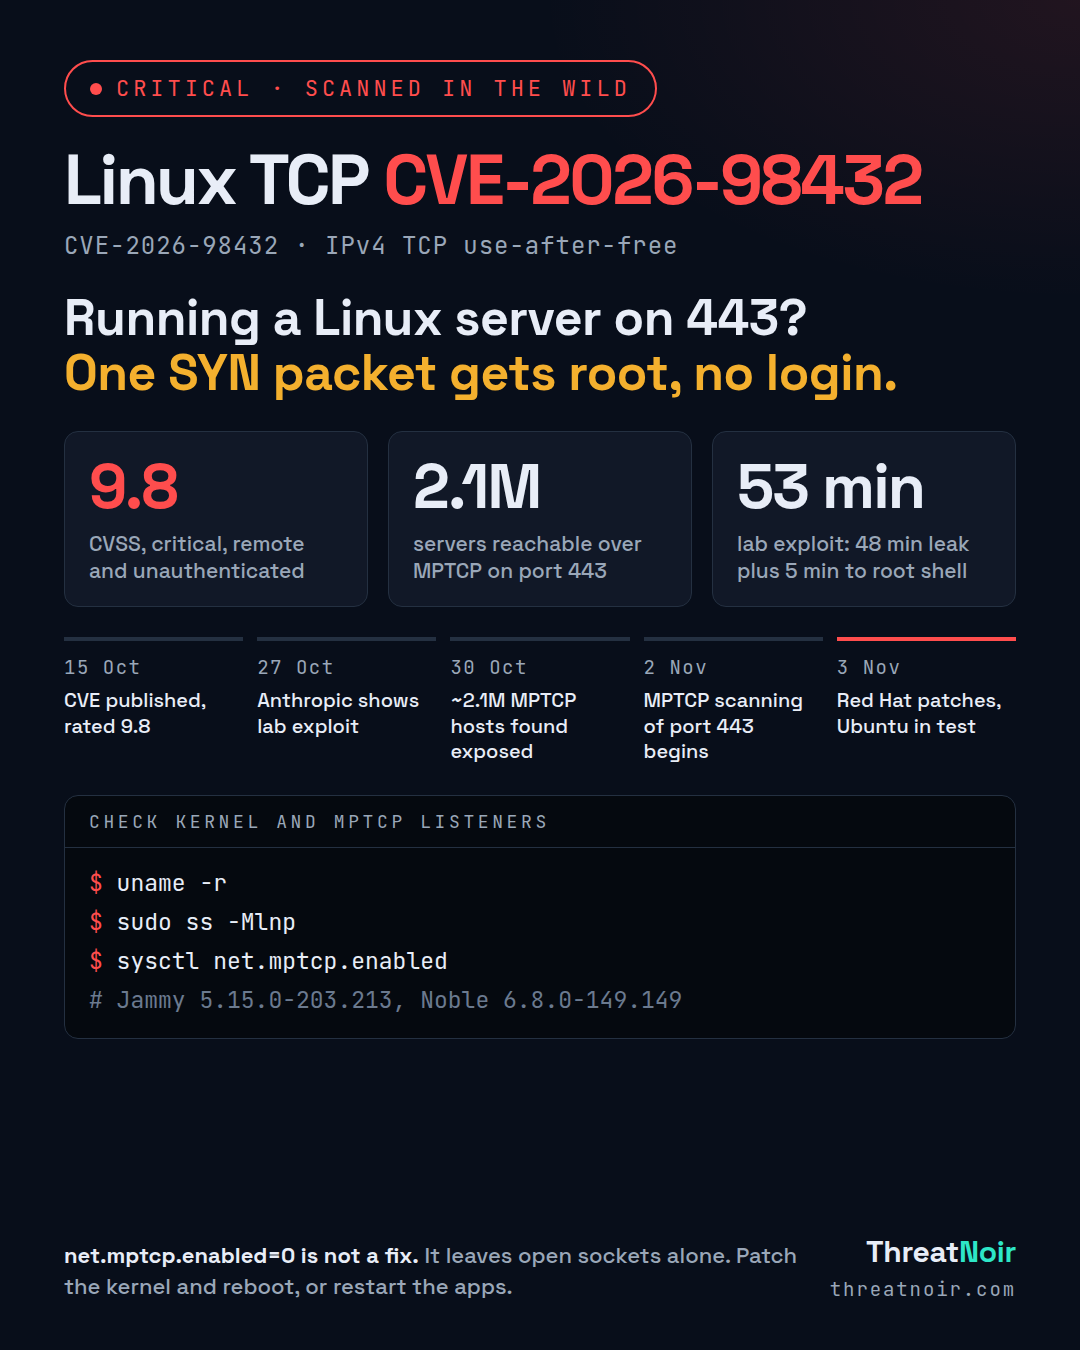
CVE-2026-98432 is a use-after-free in how the Linux kernel sets up IPv4 TCP connections. One CPU frees the IP options of a new connection while another CPU, handling a repeated SYN packet, still reads them when building a reply. That race lets a remote, unauthenticated attacker run code as root with no login and no user action.
The bug affects kernel versions 4.4 and later. The CVE record was published on 15 October 2026 and is rated 9.8, critical. Ubuntu's own blog uses the word "High" for the same score, so you may see both labels.
The upstream fix delays the free with kfree_rcu() so readers finish first.
Red Hat has released patched kernels for RHEL 8, 9 and 10. Ubuntu's fixes are still in the opt-in -proposed testing pocket, so many Ubuntu servers remain open for now.
Timeline
- 15 Oct 2026: CVE-2026-98432 published, rated 9.8.
- 27 Oct 2026: Anthropic's Frontier Red Team reports an unreleased Claude model wrote a working exploit after one prompt. In the lab the leak took 48 minutes and the shell five more. The exploit has not been released and this was a lab test, not a real incident.
- 30 Oct 2026: A scan found about 2,102,043 servers reachable over MPTCP on port 443, about 762,774 confirmed over TLS.
- 2 Nov 2026: Marcus Hutchins reports residential proxies and Russia-based VPN servers probing port 443 with MPTCP connections, which he strongly suspects targets this bug.
- 3 Nov 2026: Red Hat ships fixes. Ubuntu fixes available in -proposed.
Am I affected?
The flaw itself is not tied to MPTCP. The MPTCP link comes only from the Anthropic exploit, which targets servers with a multipath TCP listener.
Many kernels enable MPTCP by default, including Debian and others. Go 1.24 and later bind MPTCP sockets when the kernel allows it, so Go-based tools such as Caddy create the needed listener.
Ubuntu fixed versions: Jammy (22.04) 5.15.0-203.213, Noble (24.04) 6.8.0-149.149, Resolute (26.04) 7.0.0-43.43, Stonking (26.10) 7.3.0-10.10 (already in updates). Trusty (14.04) is not affected. Xenial, Bionic and Focal fixes are still pending. Focal and Bionic need Ubuntu Pro ESM; Xenial needs the Legacy add-on.
What to do now
- Run
uname -rand compare with the fixed versions above. - On RHEL 8, 9 or 10, apply Red Hat's patched kernel and reboot.
- On supported Ubuntu, you can install the -proposed kernel today if you run your own acceptance tests. Packages in -proposed are not upgraded by default, so you must name the pocket. Reboot afterward.
- List MPTCP listeners with
sudo ss -Mlnpto see your exposure. - For hosts you cannot patch yet, Ubuntu's tracker gives an nftables rule that drops incoming IPv4 TCP packets carrying IP options. It reduces risk but does not fully prevent exploitation, and it breaks any connection that relies on IP options.
How to hunt
- Look for inbound MPTCP connections to port 443 from residential proxy ranges or Russia-based VPN servers, dated from 2 Nov onward. Normal scanners do not use MPTCP by default.
- Enumerate processes holding MPTCP sockets with
sudo ss -Mlnpand check which services expose them. - Note that a lost race only fails the handshake and does not crash the host, so failed attempts leave little trace and attackers can retry.
What does not help
- Setting
net.mptcp.enabled=0does not close sockets that are already open, so affected apps must be restarted for it to take effect. - Confirming a host is reachable over MPTCP proves exposure only, not that the kernel is unpatched. Updates are the only proper fix.
Sources
- Attackers Started Scanning in the Wild for Linux Kernel RCE Flaw, Ubuntu Releases Fixes, Cyber Security News, 3 Nov
- Red Hat Patches 9.8-Rated Linux TCP RCE Flaw While Ubuntu Releases Fixes for Testing, The Hacker News, 3 Nov