ThreatNoir
Daily Brief

AI-filtered cyber intelligence for security practitioners.

Morning & Evening briefings. No noise. Just signal.

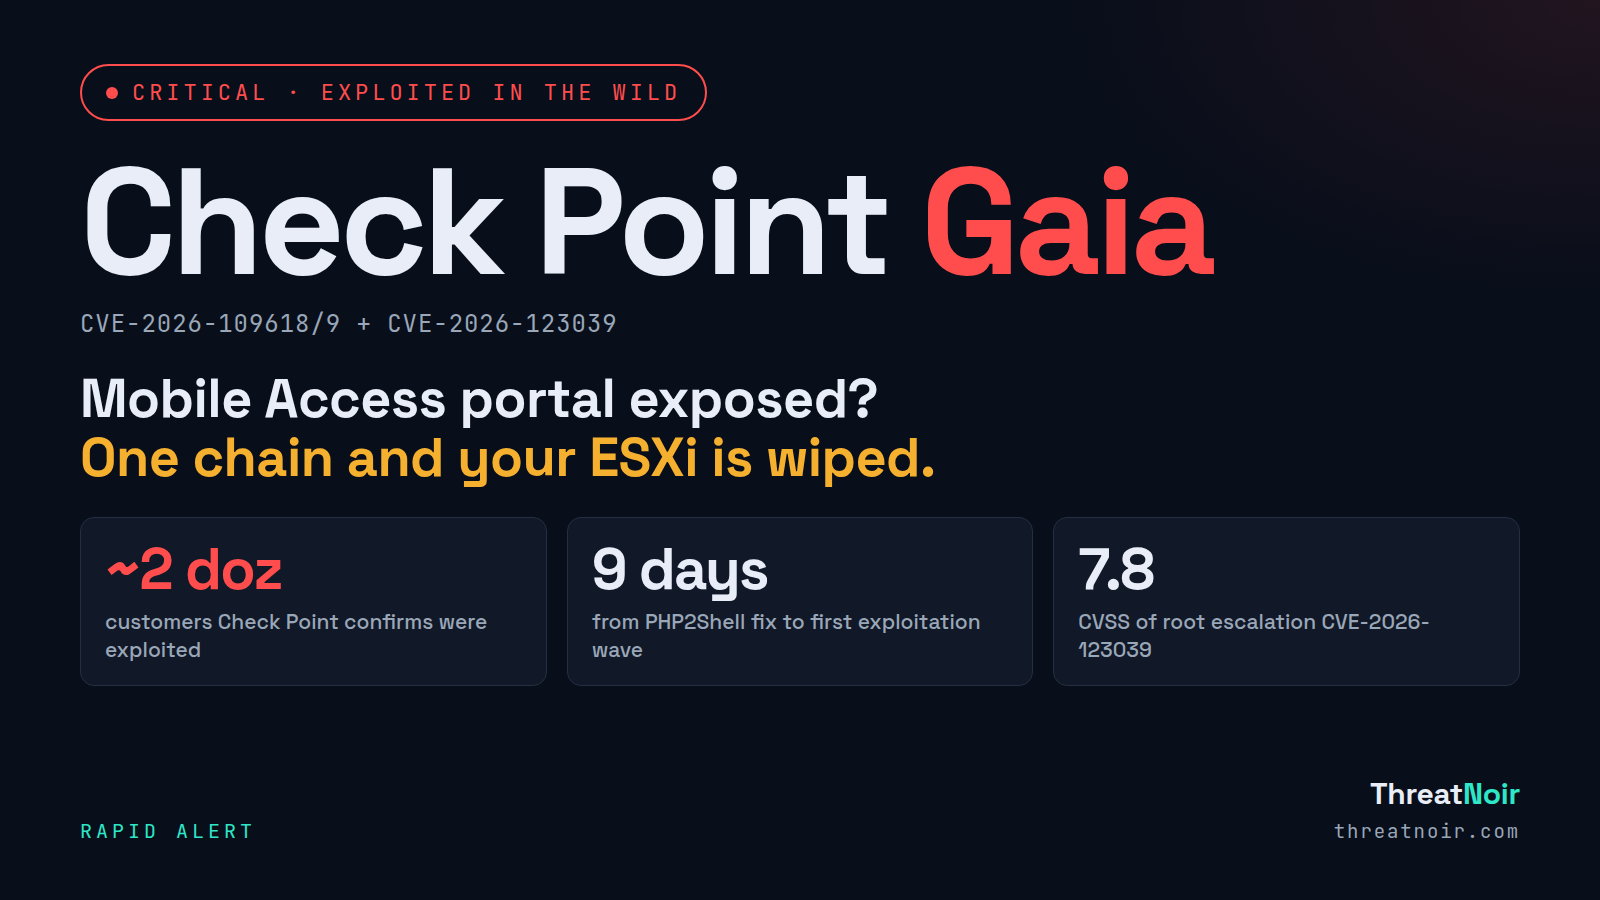
Check Point Gaia rapid alert card
Top story · Rapid alert 13 Nov

Check Point Gaia under attack: PHP2Shell chained to root for ESXi wiper, patch now

Attackers are chaining PHP2Shell (CVE-2026-109618/9) with a DynamicCLI root flaw (CVE-2026-123039) on Check Point Mobile Access gateways, then wiping VMware ESXi hosts. Patch and hunt tonight.

What to do now
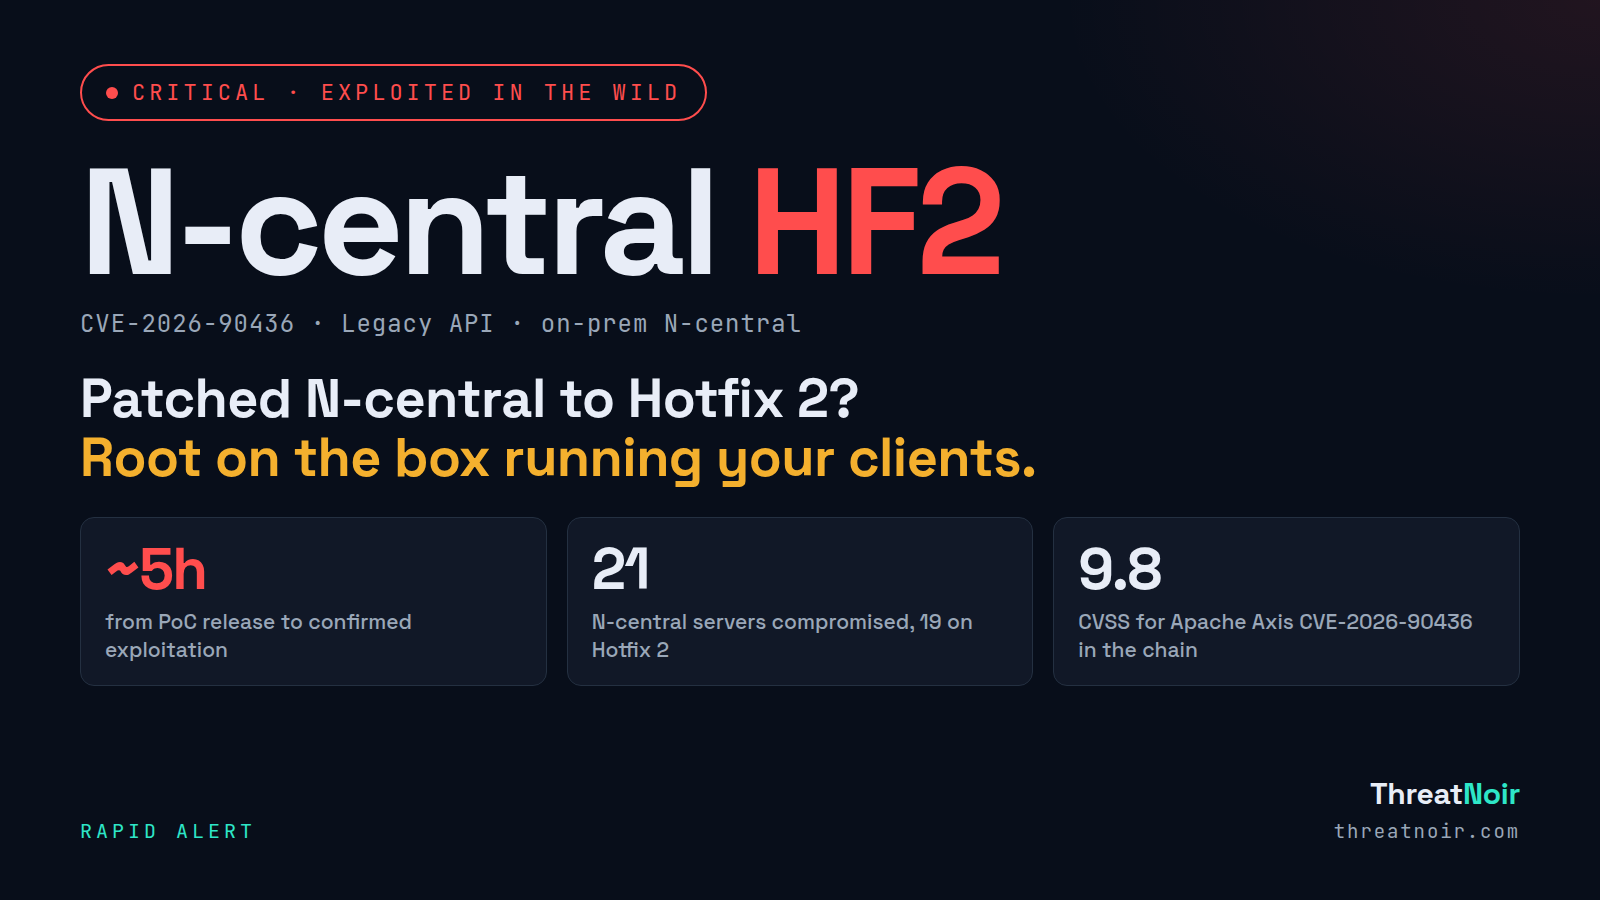
N-central HF2 rapid alert card
Top story · Rapid alert 13 Nov

4EverAble2Shell: N-central Hotfix 2 Servers Taken to Root Hours After PoC Dropped

A new N-able N-central exploit chain, 4EverAble2Shell, gives unauthenticated root on servers running the latest Hotfix 2. Attackers began mining within hours of the PoC, hitting 21 servers, 19 of them patched. Disable Legacy API and take on-prem N-central offline now.

What to do now

Latest Briefs

View all briefs
Morning Brief
November 13, 2026 · 4 stories

US seizes North Korean APT38 infrastructure, $1.2B Binance theft

  • N-able N-central zero-day exploited hours after PoC
  • Critical Apache HTTP/2 race condition RCE
  • Patch Tuesday fallout and the power of asking questions
Read full brief
Evening Brief
November 13, 2026 · 4 stories

Check Point gateways exploited and wiped via PHP2Shell

  • SignDrop zero-day abuses Windows Defender mitigation
  • ArcticRAT hides behind a black screen on Android
  • N-central zero-day exploited hours after PoC
Read full brief

Newest headlines, machine-sorted

Software rates every story from our sources for relevance. These are the newest it rated 8 or higher out of 10.

  1. German military drone operations disrupted by cyberattack
    · BleepingComputer
  2. The Take-Home Test That Runs on Your Work Laptop: Inside the AccuraSoftHire Fake Interview Campaign
    · StepSecurity
  3. PostgreSQL Patches 52 Flaws, Including 22-Year-Old Bug Enabling Authenticated RCE
    · The Hacker News
  4. Check Point gateways hacked via PHP2Shell to deploy VMware ESXi wiper
    · BleepingComputer
  5. DOJ: Gootloader used in at least 44 ransomware attacks costing $29 million since 2018
    · The Record
  6. New TypoPrompting Attacks Turn Mistyped AI Website Addresses Into Malware Installation Traps
    · Cyber Security News
See the whole feed

This week's quiz

Five questions on last week's real incidents. About five minutes, no signup.

Take the quiz

Red vs Blue

Real attacks. Real defenses. One minute to become stronger.

View all episodes

Weekly Brief

The week in cyber, summarized.

View all weekly briefs

Week of Nov 2 – Nov 8, 2026

Nine hours from disclosure to root shell

  • OpenSSH 'SSHole' (CVE-2026-123158) was exploited within hours of disclosure, granting root access on Alpine Linux and other musl-based systems — patch immediately.
  • The ARTEX AI hacking framework is now a full threat ecosystem: exposed on 1,465 public servers, used to breach South Korean banks, steal Apple code-signing certificates, and compromise WorkOS customer data after a sandbox escape.
  • OT security entered the grocery aisle: coordinated cyberattacks on European refrigeration controllers caused mass food spoilage across supermarkets and blood banks, prompting a joint CISA/FBI/ENISA advisory.
  • Supply chain fraud hit new highs: a $133M heist at Crédit Mutuel Arkéa via a service provider, and AI deepfake CEO scams netted $129M+ across multiple targets.
Read full weekly brief
Get the weekly roundup

The week in security and what it means for your team. One email, no account needed. Privacy

Prefer a feed reader? Follow by RSS