What happened
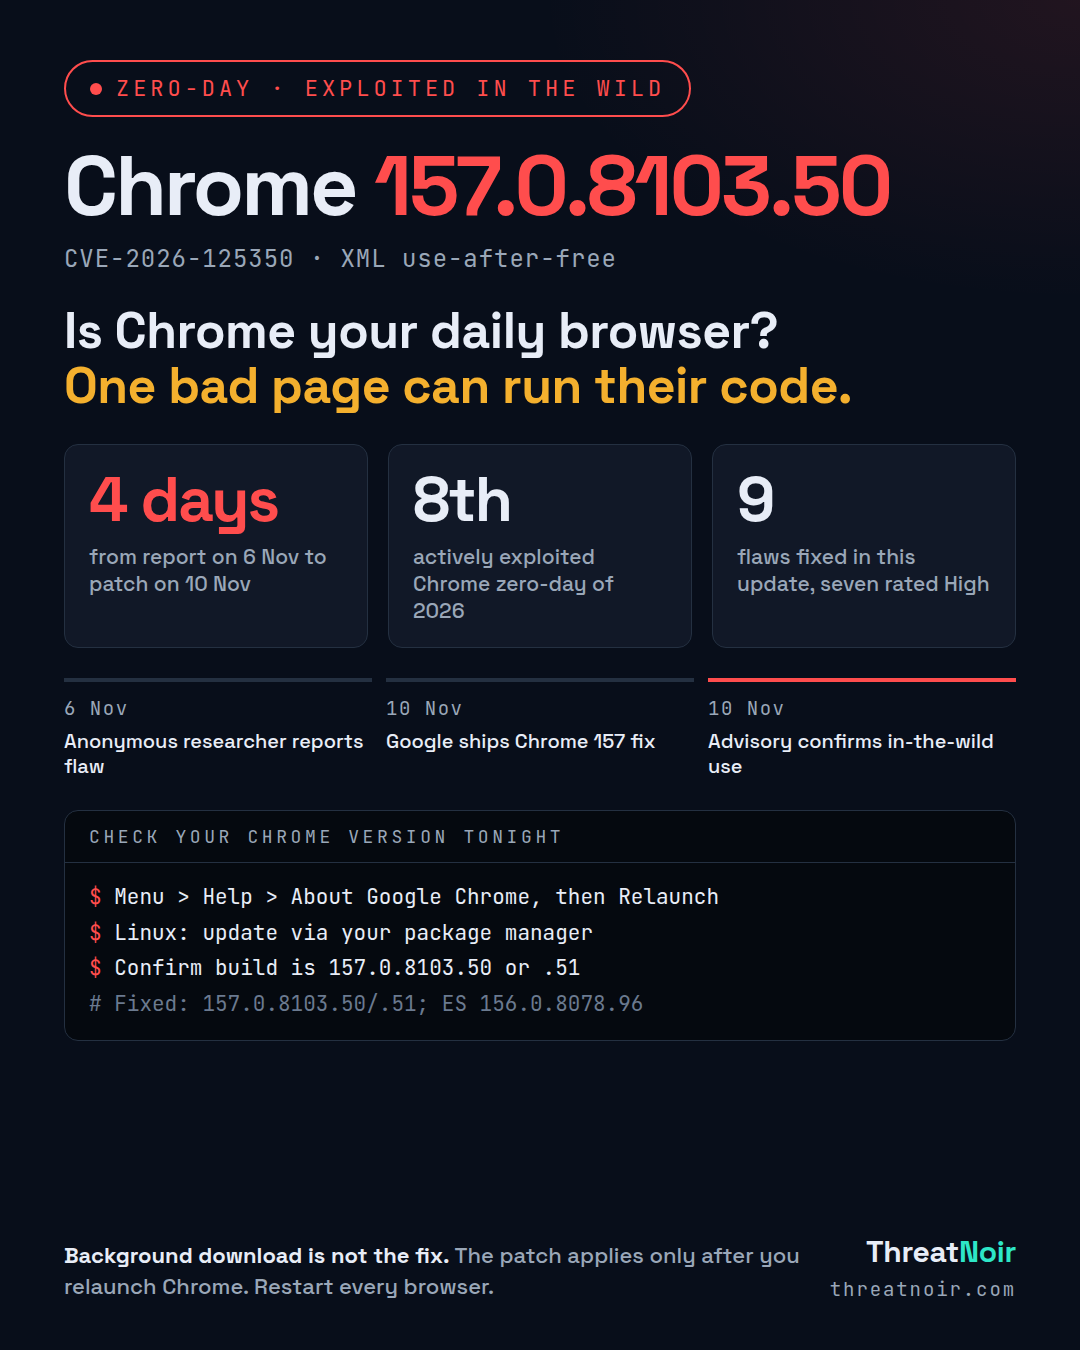
Google has released an emergency Chrome update that fixes CVE-2026-125350, a high-severity use-after-free bug in the browser's XML component. Google says it is aware that an exploit for this flaw exists in the wild. This is the eighth actively exploited Chrome zero-day of 2026.
A use-after-free happens when the browser keeps a pointer to memory it has already freed. When the XML parser later reads or writes that stale memory, an attacker can manipulate the memory layout and, under the right conditions, run their own code. The usual delivery is a booby-trapped web page reached through phishing, a malicious ad, or a compromised site. A victim may only need to open a bad link.
An anonymous researcher reported the flaw on 6 November 2026, only four days before the patch shipped. Google has not shared who is behind the attacks, how many people were targeted, or any technical detail. Access to the bug report stays locked until most users are updated. CISA has not yet added CVE-2026-125350 to its Known Exploited Vulnerabilities catalogue.
The same update fixes nine flaws in total, seven of them rated High. These include a second XML use-after-free (CVE-2026-125346), a V8 type confusion (CVE-2026-125344), a GPU out-of-bounds write (CVE-2026-125348), incorrect authorisation in FileSystem (CVE-2026-125347), a Compositing buffer overflow (CVE-2026-125343), and a WebGL uninitialised resource (CVE-2026-125345). Two medium GPU bugs round out the list.
Timeline
- 6 Nov 2026: Anonymous researcher reports CVE-2026-125350 to Google.
- 10 Nov 2026: Google ships the Stable channel fix in Chrome 157.
- 10 Nov 2026: Advisory confirms an exploit exists in the wild.
Am I affected?
You are affected if you run Chrome below 157.0.8103.50 on any desktop platform. The fixed builds are:
- Windows and Mac: 157.0.8103.50/.51
- Linux: 157.0.8103.50
- Extended Stable channel: 156.0.8078.96
Chromium-based browsers share the same engine code, so Microsoft Edge, Brave, Opera, Vivaldi and others are likely to need the same fix once their vendors ship it.
What to do now
- On every machine, open the menu, choose Help, then About Google Chrome. Chrome downloads the update in the background, but the fix only takes effect after a relaunch.
- Click Relaunch and confirm the version reads 157.0.8103.50 or .51 (desktop) or 156.0.8078.96 on Extended Stable.
- On Linux, update through your package manager and restart Chrome.
- For managed fleets, push the updated version through your enterprise policy or software deployment tool and force a restart. Do not rely on users to relaunch.
- Watch for and apply updates to every Chromium-based browser in your estate as vendors release them.
How to hunt
Google has published no indicators of compromise and no detail on the attack chain, so detection is limited. Practical steps:
- Inventory Chrome and Chromium browser versions across your fleet and flag anything below the fixed builds.
- Prioritise users who browse widely or handle sensitive data, since the vector is a crafted web page.
- Review proxy and DNS logs for the days before patching, looking for visits to newly registered or suspicious domains tied to phishing or malvertising.
- Treat any unexplained Chrome crashes around this window as worth a closer look, since use-after-free exploitation can cause crashes.
What does not help
- Assuming the background download already protects you. The fix is not live until Chrome restarts.
- Patching Chrome but leaving Edge, Brave, Opera or Vivaldi untouched. They run the same engine and need their own vendor updates.
Sources
- Chrome Update Patches Exploited XML Zero-Day, Eighth This Year, SecurityWeek, 10 Nov
- Google Chrome 0-Day Vulnerability in the Wild to Execute Malicious Code Remotely, Cyber Security News, 10 Nov
- Google fixes the eighth actively exploited Chrome zero-day of 2026, Security Affairs, 10 Nov
- Google patches eighth Chrome zero-day exploited in attacks this year, BleepingComputer, 10 Nov
- Google Issues Chrome Security Update for Eighth Actively Exploited Zero-Day of 2026, The Hacker News, 10 Nov