What happened
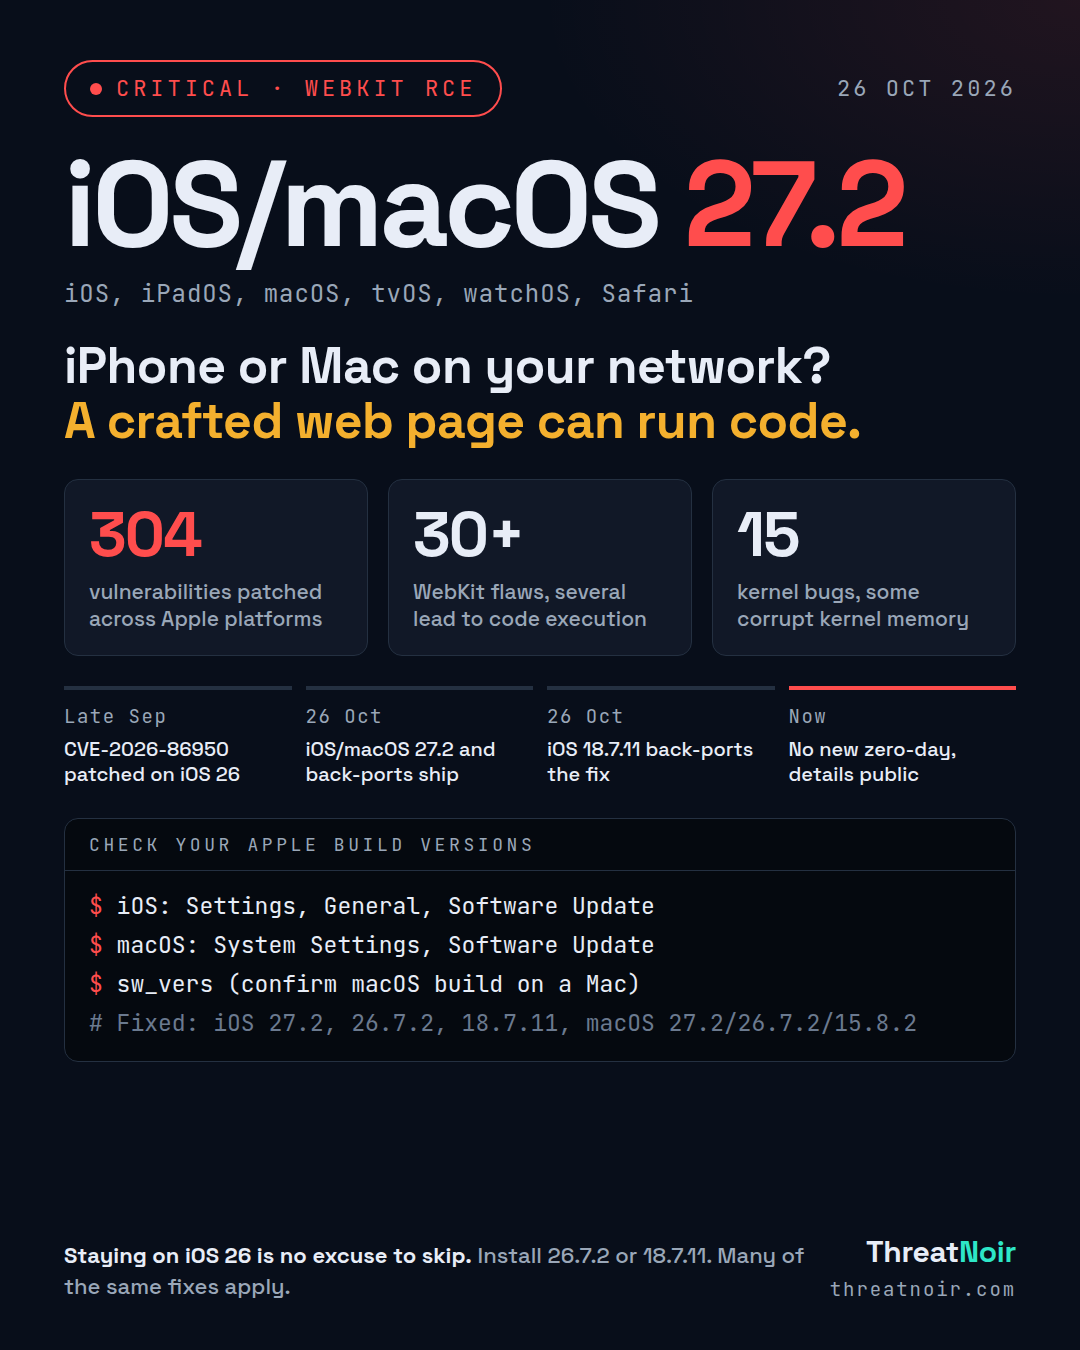
On 26 Oct 2026 Apple released its October security updates across every platform. The SANS Internet Storm Center counts 304 vulnerabilities patched. SecurityWeek puts the total at 286 across the newest iOS and macOS, with roughly 140 shared between them.
The headline risk is WebKit, the engine behind Safari and most in-app browsers on Apple devices. Apple credits more than 30 WebKit issues. Several can lead to code execution if a user opens a crafted page, including use-after-free bugs CVE-2026-112697, CVE-2026-112655, CVE-2026-112651 and CVE-2026-112623, and a type confusion bug CVE-2026-112659. Two sandbox escapes raise the stakes: CVE-2026-113897 and CVE-2026-112690 can let a remote attacker break out of the WebContent sandbox.
Apple does not list any new vulnerability as exploited in the wild. The one known exploited flaw, CVE-2026-86950 in CoreGraphics, was first patched in late September. This month's update back-ports that fix to iOS and iPadOS 18.7.11. iOS and macOS 27 do not appear to be affected by it.
Timeline
- Late September 2026: CVE-2026-86950 patched in iOS 26.7.1, iPadOS 26.7.1, macOS Tahoe 26.7.1 and macOS Sequoia 15.8.1 after exploitation in what Apple called an extremely sophisticated attack.
- 26 Oct 2026: Apple ships iOS and iPadOS 27.2 (163 fixes), macOS Golden Gate 27.2 (263 fixes), and back-port builds.
- 26 Oct 2026: iOS and iPadOS 18.7.11 back-port the CVE-2026-86950 fix.
- Now: no new exploited bug, but details are public and WebKit flaws have a long record of real-world abuse.
Am I affected?
Yes, if you run any current Apple device. The fixed builds are:
- iOS and iPadOS 27.2, 26.7.2, or 18.7.11
- macOS Golden Gate 27.2, macOS Tahoe 26.7.2, macOS Sequoia 15.8.2
- tvOS 27.2, watchOS 27.2, visionOS 27.2, Safari 27.2
iOS 27.2 covers iPhone 11 and later, and a wide set of iPads starting at iPad Pro 12.9-inch 4th generation, iPad Pro 11-inch 2nd generation, iPad Air 4th generation, iPad 9th generation and iPad mini 6th generation.
Devices still on iOS 26 get 26.7.2, which carries many of the same fixes. Do not skip it because you are not on the newest major release.
What to do now
- Push the update to iPhones and iPads through MDM, or tell users to open Settings, General, Software Update.
- Patch Macs: System Settings, Software Update. Take a backup before a major point release.
- Prioritise internet-facing and high-risk Macs. macOS Golden Gate 27.2 fixes a Remote Management bug (CVE-2026-112427) that a remote attacker could use for code execution, plus Screen Sharing and SMB bugs reachable over the local network.
- Patch tvOS, watchOS, visionOS and Safari where managed.
- Treat this as a priority cycle because of the WebKit code execution bugs, the sandbox escapes and the large kernel set.
How to hunt
- Inventory build versions across your fleet through MDM and flag anything below the fixed builds above.
- On Macs, confirm the build with
sw_versand compare against macOS 27.2, 26.7.2 or 15.8.2. - Review Screen Sharing and Remote Management exposure. CVE-2026-112473 lets an attacker with the legacy VNC password copy files to a Mac, so audit which Macs still allow legacy VNC passwords.
- Watch for unusual Safari or WebContent process crashes on unpatched devices, which can follow attempts to use the parsing and WebKit bugs.
- Note which devices are too old to receive 27.2 and plan replacement or network isolation.
What does not help
- Staying on iOS 26 to avoid a major version jump does not protect you. Install 26.7.2 or 18.7.11 instead.
- Assuming you are safe because nothing is marked exploited. Once details are public, unpatched phones and tablets become easier targets, and WebKit bugs have been used in targeted spyware before.
Sources
- Apple Patches for October 2026, (Mon, Oct 26th), SANS Internet Storm Center, 26 Oct
- Apple iOS 27.2 Released With Fixes for 163 Vulnerabilities, Including Fix for Critical WebKit RCE, Cyber Security News, 27 Oct
- iOS, macOS 27.2 Patch 286 Bugs; Fix for Exploited Flaw Backported to iOS 18, SecurityWeek, 27 Oct